➤Summary
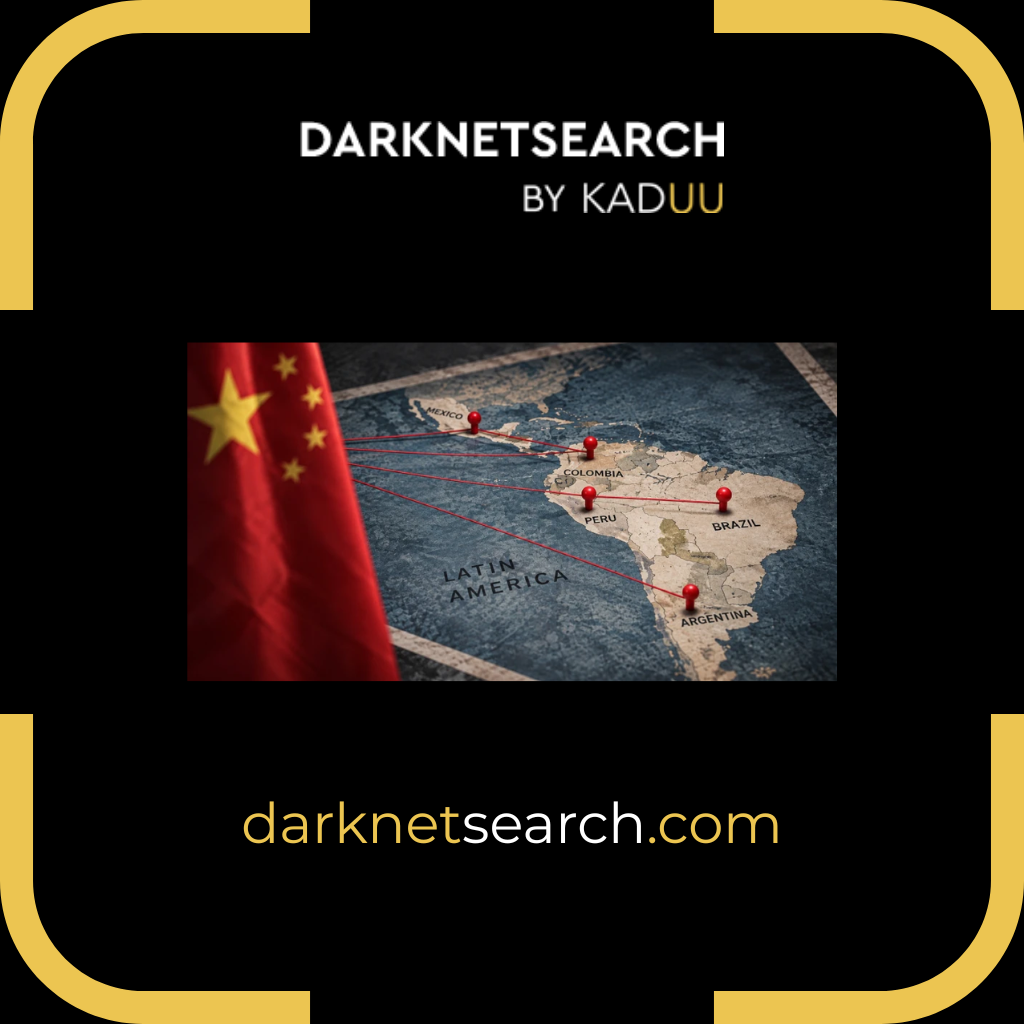
Dark web scanner intelligence can add useful context to the latest SparroWocky campaign, but it cannot replace endpoint, identity, network, or incident-response controls. ESET reports that the China-aligned espionage group FamousSparrow has used a newly identified C++ backdoor against government organizations in Latin America since at least August 2025. The activity was observed in Argentina, Ecuador, Guatemala, Honduras, Panama, Peru, Puerto Rico, and Venezuela.
The disclosure matters because SparroWocky combines broad post-compromise capabilities with anti-analysis techniques intended to make malicious activity harder for security products to interpret. Reference: ESET’s research announcement
What Happened in the SparroWocky Campaign?
ESET’s research says FamousSparrow shifted from its previously used SparrowDoor backdoor to SparroWocky around August 2025. The researchers observed the new implant in attacks against government entities across eight Latin American countries and territories, while ESET telemetry showed that 90% of the group’s targets from mid-2025 into 2026 were located in the region.
ESET assesses that the regional focus may relate to China’s interests in Latin America and to governments’ responses to increasing U.S. pressure on Chinese economic interests. That is an analytical assessment from the researchers, not evidence that every targeted organization was compromised or that a particular government directive caused an individual intrusion.
The reporting does not name affected government organizations or establish a complete victim count. Security teams should distinguish observed targeting from independently confirmed compromise.
Why SparroWocky Is Significant for Defenders
SparroWocky is described by ESET as a modular C++ backdoor incorporating code from open-source projects. Its functionality includes command and executable execution, system and network reconnaissance, file discovery and management, screenshot capture, process creation in another logged-in user’s session, and TCP proxying. It can also remove its persistence and delete files when instructed.
ESET describes runtime code patching, dynamic API resolution, call-stack and threat-origin spoofing, and techniques that disguise malicious in-memory components as legitimate Windows elements. One notable mechanism uses MinHook to intercept CreateThread so security software may see AnimateWindow rather than the original malicious entry point.
For persistence, ESET identified a Windows service named ProcAuditManager and a registry key named SnapCart. The research also identified at least 18 command-and-control addresses, communicating directly over ports 443 or 8080 or through HTTP and SOCKS5 proxies.
What Security Teams Should Monitor
A useful response should combine endpoint telemetry with identity, network, and external intelligence. Organizations investigating potential exposure should prioritize the following areas:
- Review Windows service creation and registry persistence for the artifacts identified by ESET, while treating names such as ProcAuditManager and SnapCart as investigation leads rather than standalone proof of compromise.
- Review process, network, and authentication telemetry for unexpected user sessions, processes, outbound connections, and administrative activity.
- Compare network connections with ESET’s published indicators and preserve relevant logs before retention windows expire.
- Investigate unexplained screenshots, file transfers, proxy behavior, or sensitive-data access where other indicators are present.
- Validate endpoint detections against memory-resident and anti-analysis behaviors, not only hashes or static signatures.
How a Dark Web Scanner Fits Into the Investigation
A dark web scanner addresses a different part of the risk. Endpoint telemetry can show what happened inside an environment; external monitoring can show whether related credentials, corporate data, or other exposure signals are appearing outside it.
Dark web monitoring should not be treated as proof that SparroWocky was used against a particular organization. Instead, it can help teams look for downstream exposure after a suspected intrusion, including compromised credentials, stolen session information, documents, or organizational references.
For businesses, this can help investigators check whether potentially compromised identities or corporate assets appear in external datasets, supporting credential resets, session revocation, identity investigation, and broader scoping.
DarknetSearch describes its monitoring as covering dark web and deep web sources including markets, Telegram channels, paste sites, botnet logs, IRC, social media, and other sources. Its site also describes attack-surface discovery and domain and brand protection capabilities. These are complementary visibility layers, not replacements for EDR, SIEM, MFA, vulnerability management, or incident response. DarknetSearch dark web and deep web monitoring.
For organizations evaluating an affordable dark web monitoring service, the important question is not simply how many sources a provider claims to scan. Teams should ask whether alerts can be tied to their assets, whether findings can be validated, how quickly analysts can investigate them, and whether external signals can be integrated into existing security workflows.
From Malware Detection to External Exposure Monitoring
The SparroWocky case illustrates why threat intelligence should connect internal and external observations.
A practical workflow is:
- Confirm the relevance of the observed SparroWocky indicators to the environment.
- Isolate and investigate affected endpoints according to the organization’s incident-response procedures.
- Review authentication activity and revoke or reset credentials where compromise is confirmed or reasonably suspected.
- Search external intelligence sources for related domains, identities, credentials, documents, or malware-associated indicators.
- Correlate external findings with endpoint, identity, DNS, proxy, and SIEM telemetry.
- Document confirmed facts separately from hypotheses and unverified threat-intelligence claims.
DarknetSearch’s guidance on dark web monitoring emphasizes continuous collection and analysis of underground sources to identify exposed corporate information and compromised credentials.
Domain abuse monitoring can also be useful when attackers attempt to exploit an organization’s identity after gaining information from an intrusion. Look for newly registered or lookalike domains, phishing infrastructure, and impersonation activity, then correlate those findings with known incidents instead of treating every suspicious domain as proof of an attack.
What MSSPs Can Learn From the Campaign
For MSSPs and MDR providers, the campaign reinforces the value of combining client telemetry with external threat intelligence. Providers can use malware indicators and behavioral detections internally while separately checking for credential exposure, brand abuse, and other signals that may indicate an incident has moved beyond an endpoint.
This is especially useful when one provider monitors multiple organizations. Findings can be normalized by customer, asset, identity, and threat type, helping analysts distinguish generic intelligence from exposure that directly affects a client. DarknetSearch’s threat-intelligence material describes use cases spanning SOC operations, MSSPs, and brand monitoring.
Frequently Asked Questions
What is SparroWocky malware?
SparroWocky is a modular C++ backdoor that ESET says has been used by the China-aligned FamousSparrow group against government organizations in Latin America since at least August 2025. It supports command execution, reconnaissance, file operations, screenshots, process creation, network proxying, and multiple anti-analysis techniques.
Is SparroWocky a vulnerability?
No. SparroWocky is malware, not a CVE or software vulnerability. The defensive response therefore centers on detecting and investigating the backdoor and its behaviors, reviewing persistence and network indicators, containing affected systems, and determining whether credentials or data were exposed.
Can a dark web scanner detect SparroWocky?
Not directly in the same way as EDR or malware analysis. A dark web scanner is better suited to finding external exposure associated with an incident, such as compromised credentials, leaked information, or threat-actor references. It can complement endpoint and network detection rather than replace those controls.
What should organizations do if they find related indicators?
Treat the indicators as investigation leads and compare them with endpoint, identity, and network evidence. Follow established incident-response procedures, preserve relevant telemetry, investigate persistence and outbound connections, and reset or revoke credentials when compromise is confirmed or suspected. External monitoring can then help identify downstream exposure.
Monitor What Attackers Can See
The SparroWocky campaign shows why security teams need visibility beyond a single endpoint or security product. Organizations should combine malware-focused detection with identity controls, network telemetry, attack-surface visibility, and external exposure intelligence. A dark web scanner can contribute to that broader picture by identifying information that may become useful to attackers after an intrusion.
DarknetSearch provides monitoring across dark and deep web sources and can complement an organization’s existing security operations. For teams assessing dark web monitoring for businesses, the practical objective is straightforward: turn external exposure into an actionable signal that supports investigation and remediation. Explore DarknetSearch threat intelligence and monitoring for free.
Disclaimer: DarknetSearch reports on publicly available threat-intelligence sources. Inclusion of an organization in an article does not imply confirmed compromise. All claims are attributed to external sources unless explicitly verified.
Discover how CISOs, SOC teams, and risk leaders use our platform to detect leaks, monitor the dark web, and prevent account takeover.
🚀Explore use cases →