Category: ➽Malware
-
Dark Web Search: ShinyHunters Targets Clop Leak Site
Dark web search is providing a different view of the latest conflict between two major cybercrime groups after ShinyHunters reportedly compromised and defaced the Clop ransomware operation’s leak site. The incident is unusual because the attacker and target are both established players in the cybercrime ecosystem, turning an extortion model back against the group that…
-
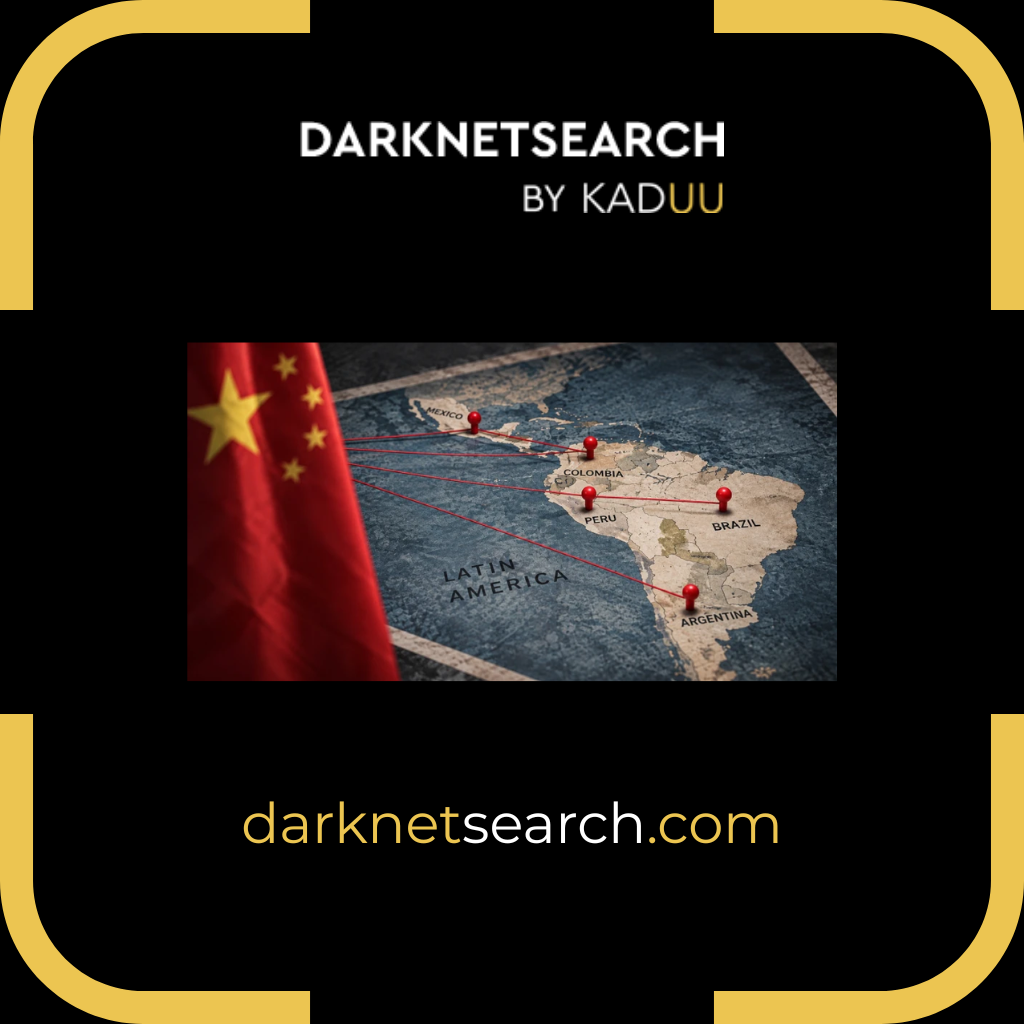
Dark Web Scanner: What SparroWocky Reveals About Espionage
Dark web scanner intelligence can add useful context to the latest SparroWocky campaign, but it cannot replace endpoint, identity, network, or incident-response controls. ESET reports that the China-aligned espionage group FamousSparrow has used a newly identified C++ backdoor against government organizations in Latin America since at least August 2025. The activity was observed in Argentina,…
-
Darknet Search Engine: Boston Scientific Cyberattack
Darknet Search Engine intelligence can provide an additional layer of visibility when a major cyber incident affects a critical medical-device manufacturer. Boston Scientific identified a cybersecurity incident on August 25, 2026, that disrupted certain information systems and business applications supporting manufacturing, order processing, and product shipments. The company is investigating the incident with third-party cybersecurity…
-
Gunra Ransomware Exploits Fortinet and Schneider Flaws
Cyber threat monitoring is the continuous process of identifying, analyzing, and responding to indicators that attackers may be targeting an organization, its infrastructure, employees, or digital assets. For modern enterprises, this means looking beyond traditional endpoint alerts and vulnerability scans to understand how emerging ransomware campaigns could translate into real-world exposure. The reported Gunra ransomware…
-
Darknet Search Engine Tracks CRPx0 Hyundai Breach
Ransomware incidents continue to create serious financial and operational risks for organizations worldwide. A single attack can disrupt manufacturing, expose sensitive business information, damage customer trust, and result in costly downtime. For security teams, identifying potential exposure before attackers weaponize stolen information has become just as important as responding to active threats. 🚨 Recent reports…
-
Dark Web Surveillance: North Korean npm Attack
North Korean threat actors have once again demonstrated how software supply chain attacks continue to evolve. Security researchers recently uncovered a malicious campaign in which attackers compromised multiple popular npm packages used by JavaScript developers. Instead of directly attacking organizations, the attackers targeted trusted software components that developers routinely install, allowing malicious code to infiltrate…
-
Dark Web Monitoring: PhantomEnigma Malware Campaign
Organizations today face increasingly sophisticated cyberattacks that abuse trusted infrastructure instead of suspicious domains. One recent example involves the PhantomEnigma malware campaign, where attackers compromise legitimate government websites to distribute malicious payloads. This tactic makes attacks significantly harder to detect because users naturally trust official government domains. Effective dark web monitoring enables organizations to identify…
-
Cyber Threat Monitoring: Russian Zimbra Zero-Day Attack
A sophisticated Russian espionage group has exploited a previously unknown vulnerability in Zimbra Collaboration Suite to steal emails, session data, and two-factor authentication (2FA) codes from targeted organizations. The campaign highlights how advanced threat actors continue to prioritize email infrastructure because it provides access to sensitive communications, credentials, and business intelligence. For organizations, this incident…
-
Dark Web Scanner: PamStealer Targets macOS Users
Businesses have long considered macOS devices to be less attractive targets than Windows systems. That assumption is becoming increasingly dangerous. The emergence of PamStealer, a newly discovered information-stealing malware distributed through a fake version of the popular Maccy clipboard manager, demonstrates that cybercriminals are actively expanding their campaigns against Apple users. Organizations relying on macOS…
-
Cyber Threat Monitoring: WeedHack Hits 116K MC
Cyber threat monitoring has become a critical defense strategy for organizations and gamers alike as cybercriminals increasingly exploit popular online communities. A recent malware campaign known as “WeedHack” infected more than 116,000 Minecraft systems, demonstrating how attackers leverage trusted gaming ecosystems to distribute malicious software 🎮. According to reports from cybersecurity researchers, the operation targeted…